CMMC Compliance in Bloomington, IL
Imagine going into your next Department of Defense contract already sure your cybersecurity meets the mark, instead of scrambling to prove it under deadline.
Walk Into Your Next DoD Contract Already Compliant
If your organization handles federal contract information or controlled unclassified information, the Department of Defense now expects you to prove your cybersecurity through CMMC. Falling short can cost you the contracts your business depends on, and the requirements are increasingly written directly into awards.
As your CMMC compliance company in Bloomington, we take you from unsure to audit-ready. We assess where you stand against the required controls, close the gaps, and build the documentation an assessor expects. You get a clear route to the CMMC level your contracts call for, without decoding the framework on your own.
What Getting Audit-Ready Includes
Gap assessments against CMMC Level 1 and Level 2 controls.
A prioritized remediation roadmap with clear costs.
Audit-ready policies, documentation, and evidence.
Support for the NIST SP 800-171 controls behind CMMC.
Secure cloud, including Microsoft GCC High where required.
Ongoing monitoring to help you stay compliant.
A local team that explains requirements in plain terms.
Facing a CMMC requirement in a contract?
We will assess where you stand and map a clear path to readiness, with no obligation.
What Bloomington Organizations Say
Fast, Reliable Support Around the Clock
Working with ETS for about a year now, I've had a great experience every time I've contacted them for support and during our new product implementation. They have been flexible when needed and quickly responsive each time we've reached out for support. Employees are great to work with, very respectful and courteous, and at understanding our issue fully before providing possible solutions. I appreciate this company and their employees.
JOSH WRYE
A Trustworthy, Transparent Partner
I could not be happier with ETS. They are always just a phone call or e-mail away to handle our IT issues 24/7. Most of my tickets have been answered AND completed within an hour. Brian has gone above and beyond to make sure we understand our options and how they are going to be implemented. ETS has exceeded my expectations. No question or project is too small or too big for them. You may also think to yourself “Do I need an IT solution?” and the answer is YES and the company is ETS.
KATIE KASSING
Proactive IT Partnership That Exceeds Expectations
We have had the privilege of working with Empowering Technology Solutions for almost two years, and I can confidently say they have exceeded every expectation we had of a managed services partner. From the outset, they demonstrated a deep understanding of both our technical requirements and the strategic objectives of our business. Their team is consistently responsive, knowledgeable, and proactive. Whether it's day-to-day support requests, complex infrastructure projects, or critical incident response, they have delivered with professionalism and precision every step of the way. Their ability to translate technical challenges into actionable business solutions has been instrumental in reducing downtime, improving security posture, and increasing operational efficiency across our organization. What truly sets Empowering Technology Solutions apart is their commitment to partnership. They don’t operate as an outsourced vendor; they function as a true extension of our internal team. Their leadership maintains regular touchpoints with our executive staff, offering transparency, forward-thinking insights, and clear roadmaps for continuous improvement. This strategic engagement has enabled us to stay ahead of emerging technologies and regulatory requirements. In a landscape filled with reactive service providers, Empowering Technology Solutions is a rare find: a proactive, value-driven partner that consistently delivers excellence. I highly recommend them to any organization seeking a reliable, forward-thinking, and results-oriented IT MSP.
JOSEPH PROVENZANO
Responsive, Professional, and Reliable Support
Empowering Technology Solutions (ETS) has been an invaluable partner in managing the IT services for our multiple specialty clinics. Their team is consistently quick to respond, ensuring that any issues or concerns are addressed promptly and effectively. Their proactive approach to IT management has minimized downtime and enhanced the overall efficiency of our operations. What sets ETS apart is their unwavering commitment to providing tailored solutions that meet our specific needs. Whether it’s a complex network configuration or routine maintenance, ETS approaches each task with professionalism and expertise. Their knowledgeable staff are always ready to offer support, ensuring our IT infrastructure remains robust and reliable. The level of service provided by ETS goes beyond just meeting expectations; they consistently exceed them. Their ability to anticipate potential issues and implement preemptive measures has saved us time and resources. It's evident that ETS values our partnership and strives to deliver exceptional service at every opportunity. We highly recommend Empowering Technology Solutions to any organization seeking a responsive, innovative, and dedicated IT service provider. Their comprehensive approach to IT management and customer-centric focus make them a standout choice for any business looking to enhance their technological capabilities.
A A.
A Truly Dependable IT Company
We were lucky enough to find ETS years ago when our current IT company couldn't help us anymore. They are an amazing company with an amazing team. They are very organized and know their field. We have many different software programs that integrate with our main software, and we never have a major issue. It has been wonderful having a company that is so dependable, especially in the IT space where so many companies don't know what they are doing. We happily get to focus on our work rather than the latest IT issue. If you are looking for a company, give ETS a call, you will be so happy you do! :)
JUDY H
in business since 2018
IT Support You Can Count On


Your Path From Unsure to Certified
Certification is a process, and rushing it wastes money. Here is how we get organizations across Bloomington ready, so preparation is steady and deliberate rather than a scramble before an award.

Measure the Gap
We measure your environment against the NIST SP 800-171 controls that underpin CMMC, then document your current score and gaps in plain, usable language.

Close What Counts
We prioritize and close gaps by risk and contract impact, from access controls and encryption to logging, so you spend on what actually moves your score.

Build the Evidence
We build the policies, the system security plan, and the evidence an assessor expects, so you are not scrambling to prove controls when the assessment arrives.

Hold the Line
Compliance is ongoing, not one and done. We monitor and review your controls, so you stay ready for reassessment and for the next contract that requires it.
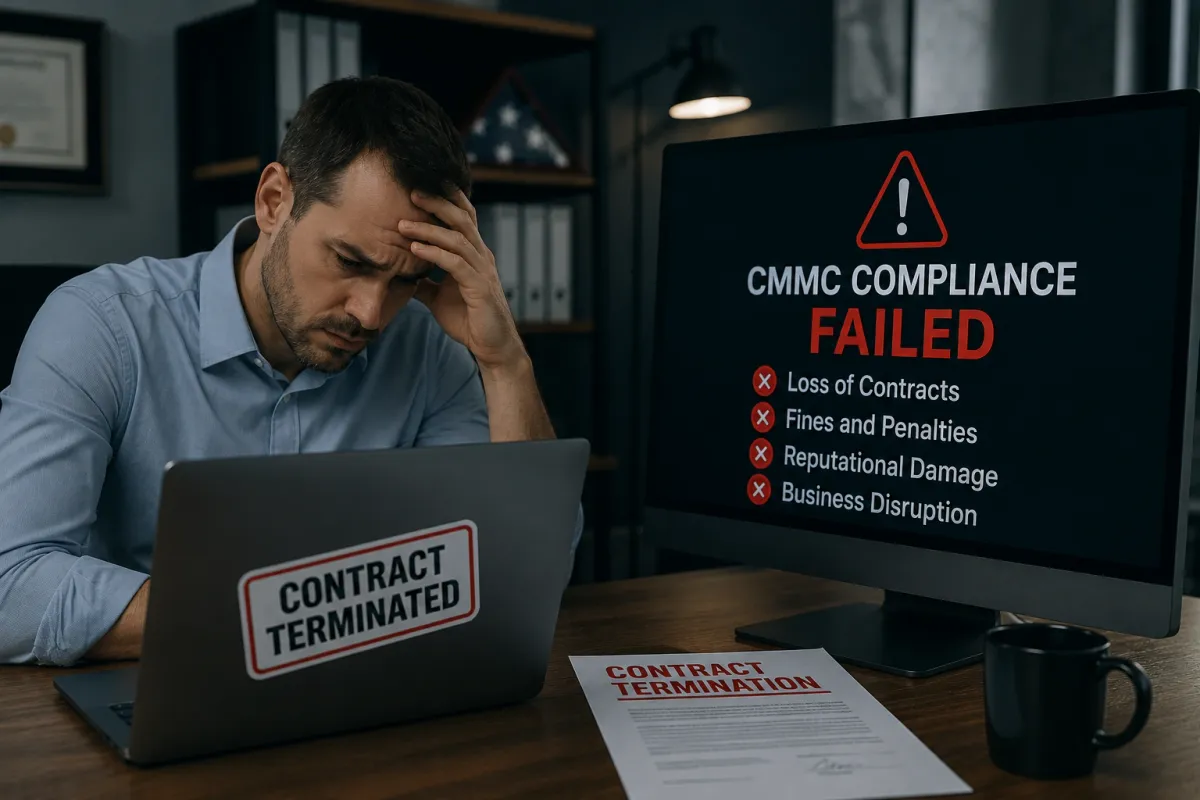
What a Missed CMMC Requirement Costs You
For suppliers in the defense supply chain, being unprepared is not a small oversight. When a contract requires CMMC and your controls are not in place, you can lose eligibility to bid, and the opportunity goes to a competitor who started earlier. The requirement often appears with little runway to react.
Getting ready cannot be rushed. Gap assessments, remediation, and documentation each take time, and trying to compress them the week before an award rarely holds up under scrutiny. Organizations that wait risk both the contract in front of them and the reputation that helps win the next one, while early movers protect their pipeline.
Want a clear path to certification?
Start early and protect your eligibility before the next award is on the line.
Compliance Built as Real Security, Not Paperwork
We approach compliance as real security, not a paperwork exercise, and that white-glove standard shapes every engagement. Each one begins with an honest assessment of where you stand, so remediation targets the controls that matter for your contracts rather than a generic checklist.
Compliance is one of our four service pillars, alongside managed services, cybersecurity, and AI, all delivered by our local IT team. We have supported organizations since 2018, now serve more than 150 clients, and hold a 96.7% customer satisfaction score, with controls mapped to official Department of Defense requirements.
Why Defense Suppliers Choose Us
White-glove service from one accountable local team.
Hands-on experience across HIPAA, SOC 2, and CMMC environments.
Controls mapped to official Department of Defense and NIST SP 800-171 requirements.
96.7% customer satisfaction across more than 150 clients served.
Microsoft 365 Solutions Partner, Sophos Platinum Partner, and Verkada Gold Partner.
Taylor Business Group Award 2024 winner and McLean County Chamber member.
What Certification Protects for Your Business
Protected Contracts
A missed requirement can cost you a bid outright. Our CMMC compliance work puts the controls and documentation in place that buyers in the defense supply chain expect, so your eligibility is protected before an award is on the line.
Smarter Spending
Trying to fix everything at once drains budgets fast. We target the gaps that actually affect your score, so investment goes where it moves you toward certification instead of everywhere at once.
Audit Confidence
Facing an assessment without evidence turns into a stressful scramble. We prepare your policies, system security plan, and evidence in advance, so you walk into the assessment ready rather than hoping.
Stronger Security
The controls behind certification are the same ones that reduce real breach risk. We harden your environment as we prepare you, so you gain protection, not just a passing score.
Ready to start your CMMC roadmap?
Get a gap assessment, a prioritized plan, and the documentation assessors expect.
Who Needs CMMC Across Bloomington
CMMC reaches every organization that touches federal contract information or controlled unclassified information, so we tailor readiness to where each one sits in the defense supply chain. Here are the organizations we help prepare for certification across Bloomington and Central Illinois:
Manufacturing
CMMC readiness for producers and suppliers in the defense supply chain.
Engineering & Aerospace
Controls for firms handling controlled unclassified information.
Professional Services
Compliance for subcontractors, partners, and service providers.
A Local Partner Through the Whole Assessment
We work from our Bloomington office at 131 N Williamsburg Dr and guide organizations throughout Bloomington, Normal, and McLean County, and across Central Illinois toward Peoria, Champaign, and Decatur. Compliance goes smoother with a local team that can sit with you through the assessment, walk your environment in person, and answer to you rather than a distant queue.
What Contractors Ask About CMMC
What is CMMC compliance?
CMMC, the Cybersecurity Maturity Model Certification, is the Department of Defense program that verifies contractors protect federal contract information and controlled unclassified information. Compliance means meeting the required level of cybersecurity controls and proving it through documentation and assessment. We guide organizations in Bloomington through CMMC compliance from first assessment to audit readiness.
How do I become CMMC compliant?
You start with a gap assessment against the required controls, then remediate the gaps, document your controls, and complete the assessment for your level. Our CMMC readiness work walks organizations in Bloomington through each step, so nothing is missed before an assessment.
How much does it cost to get CMMC compliant?
Cost depends on your current gaps, your required level, and your environment, so there is no flat figure. After a gap assessment, we give you a clear, prioritized plan with costs, so you can budget toward certification without surprises.
How hard is it to get CMMC certified?
The difficulty depends on how far your current controls sit from the required level. With a clear assessment, a prioritized roadmap, and documentation prepared in advance, our CMMC readiness work makes the process manageable rather than overwhelming.
Is NIST SP 800-171 the same as CMMC?
Not quite. NIST SP 800-171 is the set of security controls for protecting controlled unclassified information, and CMMC Level 2 is built on those controls and adds a verification and certification process. Our readiness work assesses and remediates against NIST SP 800-171 as the foundation.
What CMMC level do we need?
Most organizations need Level 1 or Level 2, depending on the type of data their contracts involve. We assess your contracts and data, then confirm the level you must meet, so you neither over-invest nor fall short.
Do you provide Microsoft GCC High?
Where your data and contracts require it, we set up and secure Microsoft GCC High as part of your compliance environment. It is a government-community cloud built for controlled data.
Not Sure Where to Start? Start Here.
If a contract hinges on CMMC and you are unsure where to start, that is exactly the moment to talk. As your local IT company, we will assess where you stand, explain which level applies to you, and map a clear path to readiness.
There is no pressure, just a straight conversation about compliance.
Not Sure Which Level Applies to You?
We will explain what CMMC requires for your contracts and outline your path to readiness.
You Deserve A Higher Quality of IT Support...
Most owners find out how thin their security was on the day it fails, and how slow their IT company is on the same day. You can find out now instead, on a call that costs nothing, from somebody who will say it plainly.
Call (702) 874-3767 today or click the button below to see firsthand what white-glove IT services look like.
Client Support
Sales Inquiries
Our Offices
Headquarters: 131 N Williamsburg Dr. Bloomington, IL 61704
Tacoma, WA: 748 Market St #203, Tacoma, WA 98402, United States
Las Vegas, NV: 2300 W Sahara Ave Ste 800, Las Vegas, NV 89102, United States